IMF and Central Bankers Warn AI-Driven Cyber Threats Risk Global Financial Stability
Financial leaders at the IMF meetings in Bangkok warned that AI-boosted cyber threats and autonomous financial agents could undermine institutional trust and disrupt the global economy.
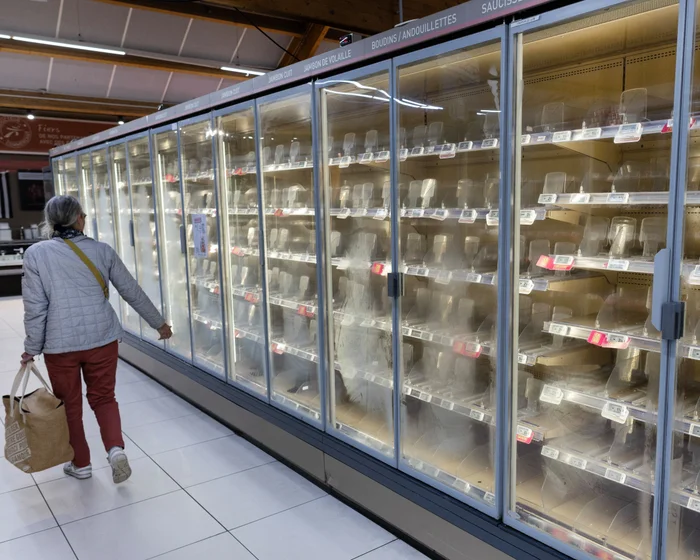
Global financial leaders gathered at the International Monetary Fund’s annual meetings in Bangkok to confront the destabilizing intersection of artificial intelligence, automated software, and cybersecurity. Discussions were punctuated by an incident in France, where supermarket chains were forced to discard vast quantities of spoiled groceries after intruders remotely altered commercial refrigerator settings up to 50C. The event highlighted how interconnected digital infrastructure has become a target for malicious disruption.
IMF Managing Director Kristalina Georgieva cautioned that AI is effectively placing the potential for digital fraud on steroids. Beyond standard market corrections or tech-driven equity volatility, financial chiefs emphasized that cybercrime accelerated by generative models threatens public faith in established financial systems. Drawing on her childhood memories from Bulgaria behind the Iron Curtain, where low institutional confidence led citizens to stash cash in shoeboxes under their beds, Georgieva warned that a failure to manage these vulnerabilities could trigger a modern retreat from mainstream banking institutions.
Systemic exposure to automated agents
The warnings from central bankers also zeroed in on autonomous software operating on consumer behalf. Meta’s Muse, for instance, has begun offering services that allow individuals to connect their financial credentials so an automated agent can locate superior interest rates and reallocate funds dynamically.
Regulators worry that widespread deployment of automated financial actors could prompt dangerous herding behaviors, moving deposits across institutions so rapidly that bank runs accelerate during market stress. Furthermore, unresolved legal questions surround who absorbs the liability when an autonomous tool makes a flawed or unlawful transaction. JP Morgan chief executive Jamie Dimon announced that his firm would restrict automated agents from operating on customer accounts, warning against the proliferation of thousands of uncontrolled rogue agents.
Physical devices also face heightened exposure. Andrew Bailey, Governor of the Bank of England and chair of the Financial Stability Board, highlighted disclosures from Anthropic warning that AI models could eventually gain the ability to self-replicate across networked household appliances. Bailey noted that if consumer confidence in monetary systems dissolves, basic societal functions break down. In response to mounting concerns, G7 finance ministers announced in Bangkok that they will conduct cyber resilience simulations, while the UK intends to center AI safety during its upcoming G20 presidency.
At the same time, policy friction persists. In the United States, Federal Reserve Chair Kevin Warsh echoed the administration's mandate to refer to AI as superintelligence. Jay Clayton, heading a federal superintelligence taskforce, has initiated mechanisms requiring laboratories to disclose breaches, jailbreaks, and intrusions, though the framework lacks mandatory pre-deployment testing.
What it means for developers
For engineering teams building AI agents, financial integrations, and connected hardware, the Bangkok discussions signal tightening oversight and emerging operational friction.
Stricter Access Controls from Enterprise Platforms: With major institutions like JP Morgan actively prohibiting third-party automated agents from transacting on client accounts, developers building personal finance bots cannot rely on open API access or automated screen-scraping. Applications handling automated transactions will face heightened authentication barriers, restrictive rate limits, and verification requirements to prove they are not acting as rogue actors.
Compliance Focus on Safety Disclosures: The shift by regulators—including the reporting mandates introduced by the US taskforce and resilience testing by the G7—indicates that incident reporting for jailbreaks, prompt exploits, and security flaws will transition from voluntary responsible disclosure to mandatory regulatory compliance. Teams deploying models interacting with critical infrastructure or sensitive user data must establish rigid auditing and audit logging pipelines.
Defensive Model Evaluation: As concerns mount around autonomous tool misuse and replication across edge devices, developers need to test system behavior across multiple base models to assess reliability and vulnerability profiles. Developers evaluating security safeguards and agentic frameworks can test top AI models cheaply through one API at https://apixoai.online to benchmark latency, cost, and safety guardrails across diverse model providers.
Liability and Autonomous Constraints: The legal ambiguity surrounding agent decisions means developers should avoid fully autonomous financial execution loops. Implementing human-in-the-loop approvals, deterministic transaction ceilings, and clear attribution logs will be essential to protect services from legal exposure if an underlying model misinterprets instructions.
Source: World leaders must wise up to threat of cyber-attacks or rogue fridges will be least of their worries — The Guardian AI. Written by the Apixo team from that report.
One key for Claude, GPT, GLM, DeepSeek and more. Pay per token with crypto.
Get your API key