Cybersecurity Leaders Outline Practical Defenses Against AI-Driven Cyber Threats
At Secure Delaware, security leaders detailed how AI is compressing vulnerability exploitation from weeks to hours and why core security fundamentals remain the primary defense.
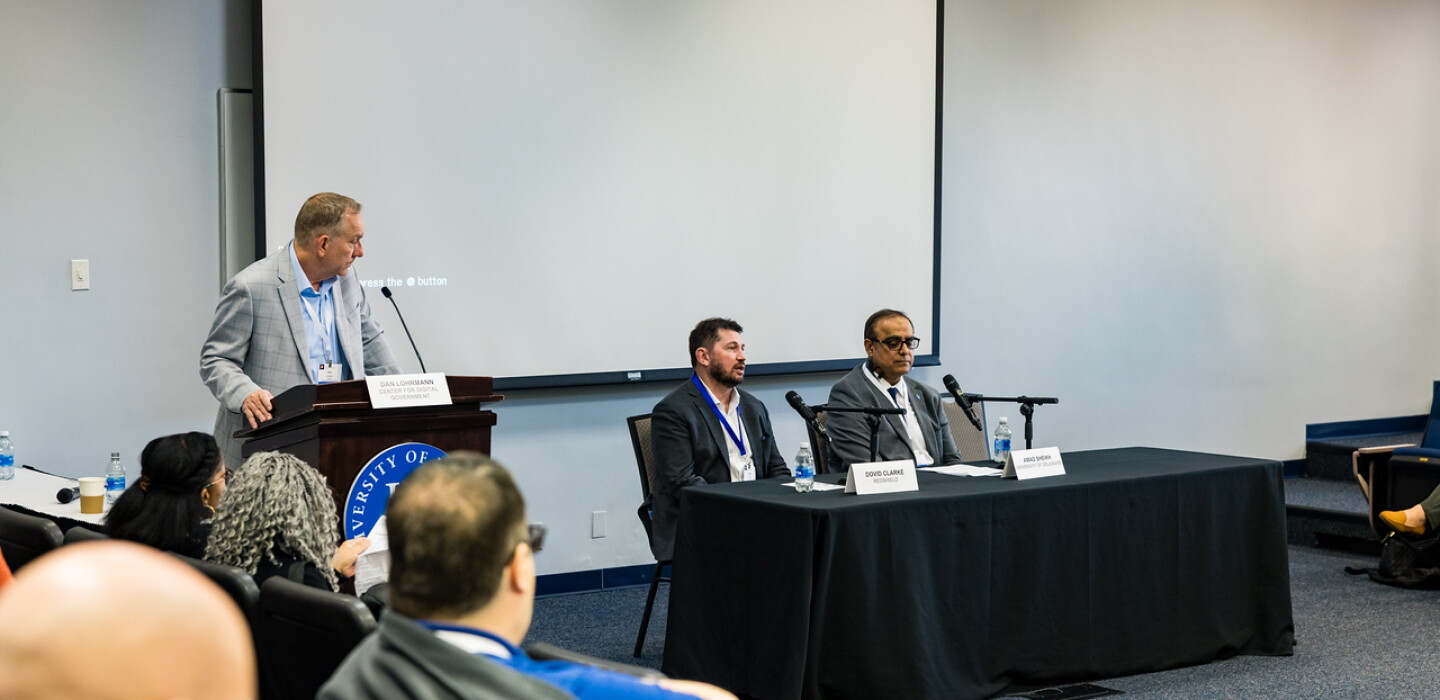
At the Secure Delaware conference hosted by Government Technology, cybersecurity leaders gathered to assess how artificial intelligence is reshaping institutional risk. During a session titled "Combatting the Artificially Enhanced Threat Actor," panelists Dovid Clarke, CEO of RedShield, and Amad Sheikh, Chief Information Security Officer at the University of Delaware, joined the conference moderator to evaluate how automated tooling is altering the balance between attackers and defenders. When asked if AI-enabled adversaries are actively transforming cybersecurity risk and forcing organizations to adjust defensive priorities, the clear consensus in the room was affirmative.
The discussion highlighted a shifting operational landscape where both attackers and public-sector institutions are leaning more heavily into automation. Examples shared across government and university environments spanned from unvetted AI deployments and shadow AI concerns to unsecured models on platforms like Hugging Face and an expanding wave of AI-assisted ransomware.
Separating AI Velocity from Sci-Fi Hype
Security teams frequently struggle to separate genuine operational threats from exaggerated marketing claims. According to the panel, the tangible danger of AI does not lie in science-fiction scenarios like fully self-driving, autonomous cyber breaches or automatic zero-day discovery. Those capabilities remain rare and heavily overstated.
Instead, the genuine impact of AI stems from volume and velocity. Adversaries use machine learning to automate social engineering and scale targeted phishing campaigns, lowering the technical threshold required for less-skilled attackers to conduct effective campaigns. The most significant shift occurs after a vulnerability is publicly disclosed. Historically, defenders had weeks between disclosure and the arrival of weaponized exploits. With generative and automated tooling, adversaries can generate exploits almost instantly, compressing that window down to hours. Defenders constrained by manual testing procedures and rigid change windows now face an asymmetrical race against machine-speed attacks.
Refocusing on Threat-Informed Fundamentals
To counter this acceleration, the panelists emphasized that organizations cannot afford to abandon core security hygiene in pursuit of novel tools. Rather, automated threats make traditional fundamentals far more critical. Rigorous asset management and strict identity and access controls serve as the primary barriers preventing automated lateral movement across a network. Alongside robust asset visibility, maintaining rapid patch management and continuous backup verification ensures that organizations can recover even when fast-moving exploits bypass exterior perimeters.
Prioritization must also evolve. Rather than relying solely on static CVSS metrics, security teams are encouraged to adopt threat-informed prioritization based on active exploitation data. Focusing rapid patching and isolation on exposed, high-risk external assets allows public-sector and educational institutions to manage attack surfaces more effectively with limited staff.
Furthermore, the panel underscored the value of collective defense networks. Information-sharing groups such as REN-ISAC and MS-ISAC enable universities and state, local, tribal, and territorial entities to pool threat intelligence. By converting single detections into shared blocklists and coordinated playbooks, institutions can mitigate machine-speed threats collaboratively rather than attempting to defend in isolation.
What it means for developers
For software engineers and system architects, the compression of vulnerability timelines requires a fundamental rethink of patching, asset management, and exposure. With attackers weaponizing newly published vulnerabilities within hours, engineering teams can no longer depend on slow, manual deployment cycles to patch critical dependencies and exposed endpoints.
Key takeaways for engineering and application teams include:
- Tighter Control Over Machine Assets: As automated scans quickly identify external-facing interfaces, developers must maintain strict inventories of APIs, microservices, and external dependencies to prevent unmonitored systems from becoming easy entry points.
- Governing Internal Model Usage: Unregulated use of third-party models from repositories like Hugging Face introduces shadow AI risks into institutional environments. Development teams need standardized policies for sourcing, testing, and sandboxing machine learning components.
- Identity as a Boundary: Because machine-speed exploits aim for fast lateral traversal, engineers should implement strict least-privilege access and identity controls within service layers and microservice architectures.
- Designing for Rapid Updates: Build pipelines must support rapid, continuous testing and immediate remediation, minimizing the friction between vulnerability identification and production deployment.
As development teams build and evaluate modern software environments, integrating reliable AI components safely remains essential. Teams looking to experiment across multiple architectures can try top AI models cheaply through one API at https://apixoai.online, allowing engineers to benchmark different models under structured, monitored access.
Ultimately, as the panelists concluded, defending against AI-enhanced adversaries does not require reinventing cybersecurity. It demands that organizations treat AI as an operational risk multiplier, communicate risks to executive leadership based on real-world business impacts rather than speculation, and reinforce the human, process, and technical fundamentals that keep core systems resilient.
Source: How Can Organizations Combat the AI-Enhanced Threat Actor? — GovTech AI. Written by the Apixo team from that report.
One key for Claude, GPT, GLM, DeepSeek and more. Pay per token with crypto.
Get your API key