IBM and CoreWeave Collaborate on Infrastructure Controls for AI Agent Workloads
IBM Research and CoreWeave are co-engineering identity management, sandboxes, and workload isolation to support the shift from model training to active AI agent testing.
As artificial intelligence development shifts from static model pre-training to running autonomous agents that execute code and interact with external systems, the underlying infrastructure requirements are changing rapidly. High-performance compute environments initially designed for massive matrix multiplication must now safely handle complex execution stages, tool integrations, and dynamic storage requests. To address these demands, IBM Research has partnered with specialized cloud provider CoreWeave Inc. to co-design workload isolation and identity management controls tailored for agent-based workflows.
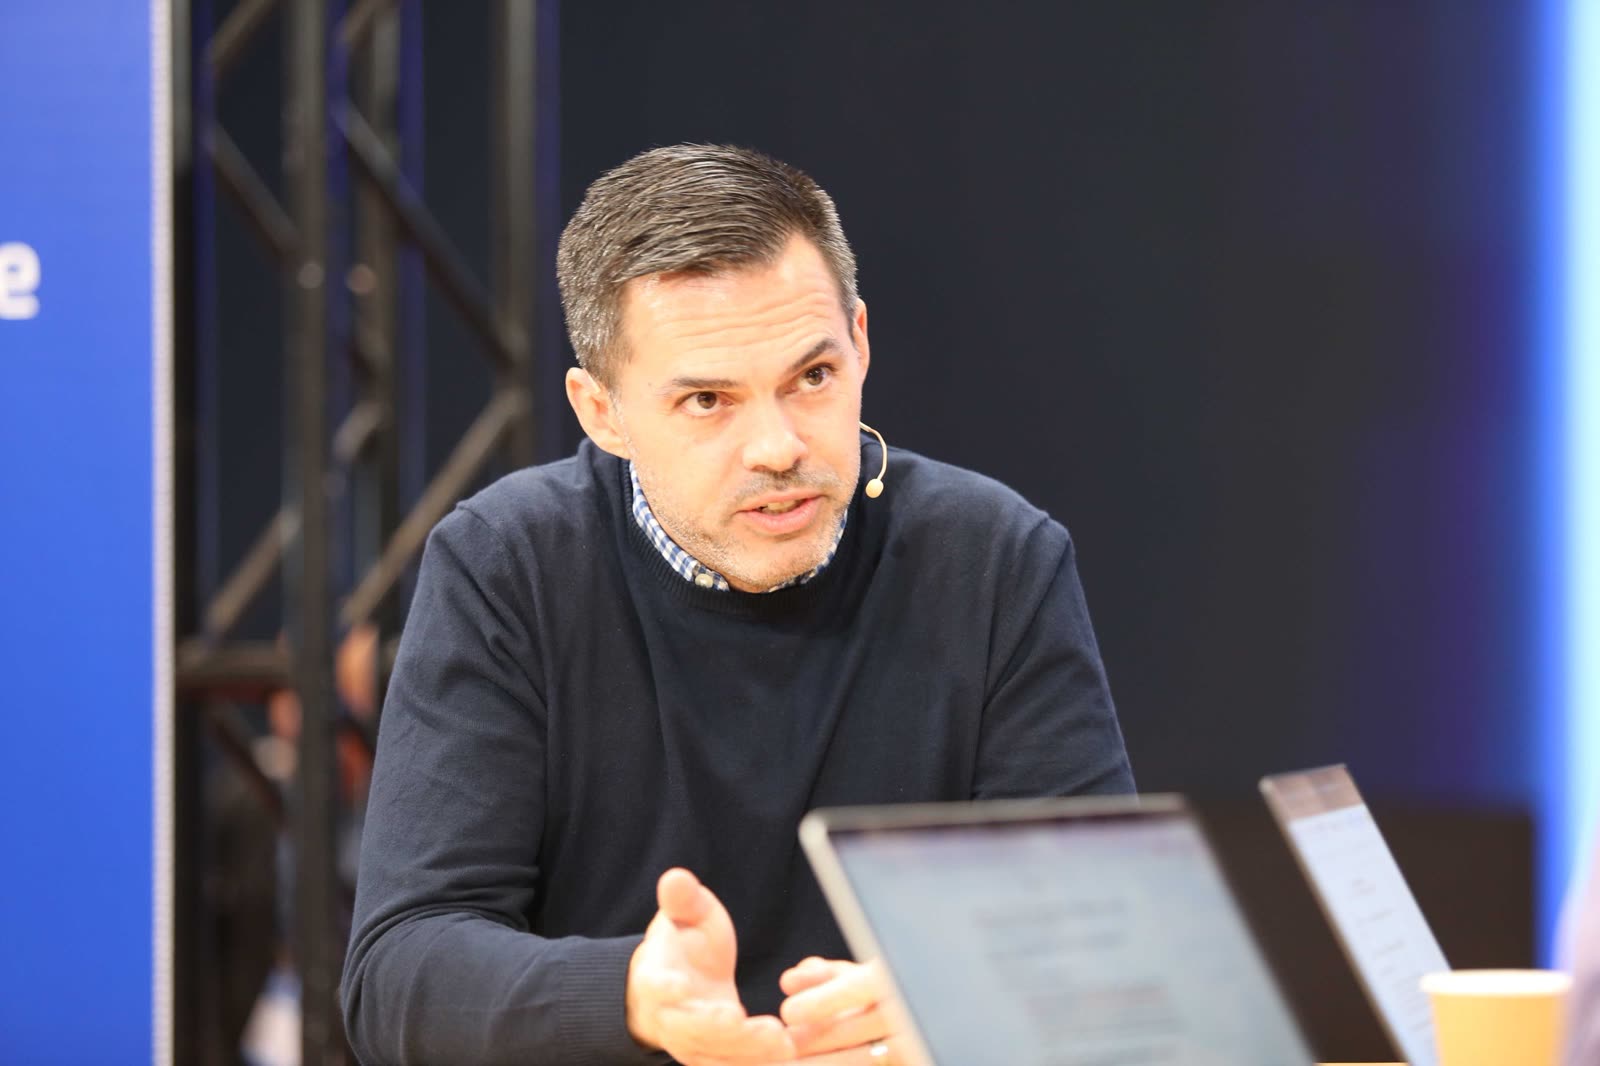
Speaking at the Fully Connected event, Brian Belgodere, senior technical staff member at IBM, detailed how modern research methodologies—such as reinforcement learning (RL)—fundamentally alter compute needs. Unlike traditional training pipelines that run uninterrupted batch jobs, RL workflows require taking intermediate model checkpoints, deploying them directly into inference environments, and assigning them active tasks to measure performance. This iterative testing introduces unpredictable execution profiles and security boundaries into compute clusters.
The shift from raw model training to active agent execution
IBM Research's work developing its Granite family of foundation models initially required substantial compute power. When planning for subsequent hardware generations, the physical cooling and power requirements led IBM to establish an extensive Nvidia H100 cluster inside CoreWeave's specialized infrastructure. According to Belgodere, IBM built out the setup end-to-end to ensure the environment could handle intensive research workloads.
Over time, the partnership evolved beyond raw GPU hosting into collaborative systems engineering. The shift toward agentic systems means models are frequently instructed to generate and execute code, connect to external toolsets, and query storage. To secure this process, IBM shared its internal enterprise identity requirements with CoreWeave, iterating on designs that bridge IBM's existing identity systems directly into CoreWeave’s infrastructure environment.
Sandboxing and the security-performance tradeoff
To manage isolation, IBM uses a largely single-tenant footprint with dedicated storage deployed within CoreWeave, while maintaining the ability to spin up additional capacity based on security and budget parameters. A central component of this setup is CoreWeave Sandboxes, which provide isolated environments for executing agent code either on dedicated hardware or through a managed serverless runtime.
These sandboxing mechanisms allow research teams to define precise boundaries around what resources an autonomous agent can access during test phases. However, implementing strict isolation introduces overhead. IBM systematically benchmarks the performance impact of its security controls to balance throughput with safety.
Belgodere described AI security as an end-to-end supply chain challenge that spans hardware, firmware, operating system kernels, training data provenance, container images, and autonomous agent code. Making incorrect architectural choices early on—such as misjudging isolation layers or over-allocating networking infrastructure—can lead to costly retrofits later in the development lifecycle.
What it means for developers
For developers building autonomous agents, the collaboration between IBM and CoreWeave highlights the importance of workload isolation and environment controls when models move from generation to execution. When an AI agent generates code or invokes APIs, running that code in unprotected environments creates significant operational and security risks. Incorporating sandboxed execution environments, identity boundaries, and explicit provenance tracking is becoming a standard design requirement.
At the same time, building complete agent pipelines requires evaluating how different foundation models perform in task-execution and tool-calling scenarios. Teams looking to test agent capabilities without building out dedicated GPU clusters can experiment with leading foundation models through unified platforms. Services like Apixo provide developers with low-cost, pay-per-token API access to models from providers like Anthropic, OpenAI, Google, and DeepSeek using a single API key, allowing engineers to benchmark model logic before deploying complex runtime sandboxes.
As infrastructure providers formalize runtime isolation and enterprise identity controls, developers can expect more standardized tools for deploying agents safely in both serverless and dedicated environments.
Source: IBM and CoreWeave co-design controls for agent workloads — SiliconANGLE AI. Written by the Apixo team from that report.
One key for Claude, GPT, GLM, DeepSeek and more. Pay per token with crypto.
Get your API key